A supply-chain attack targeting Optimizely injected malicious JavaScript into customer projects and caused malware to load on websites operated by major organizations, including Zoom, CNN, Fox News, BBC, Salesforce, GitLab, KLM, Air France, and others.
The malicious code was designed to steal cryptocurrency, capture payment-card data, collect browser information, and deliver exploit frameworks targeting vulnerable iPhones and iPads.
Optimizely Vulnerability Enabled JavaScript Injection
Optimizely is a digital experimentation and personalization platform whose JavaScript components are embedded in customer websites.
Attackers exploited a vulnerability in the platform’s Experimentation account signup flow to inject malicious JavaScript into affected customer projects.
Optimizely said it blocked the vulnerable path, deployed a fix, removed injected code from affected projects, terminated active sessions, revoked tokens, reset affected accounts, and prevented malicious code delivery through Cloudflare.
Hundreds of Optimizely Scripts Were Compromised
Security researcher Scott Helme identified 188 compromised Optimizely JavaScript files belonging to 178 organizations after analyzing more than 1,600 scripts.
Affected websites included major media, technology, retail, financial, aviation, nonprofit, and SaaS brands.
The compromise demonstrates the scale of risk associated with third-party JavaScript supply chains: a single trusted platform can become a delivery mechanism for malicious code across many unrelated websites.
Salesforce disabled Optimizely scripts across preview and production environments while investigating the incident.
Malicious Script Loaded Secondary Payloads
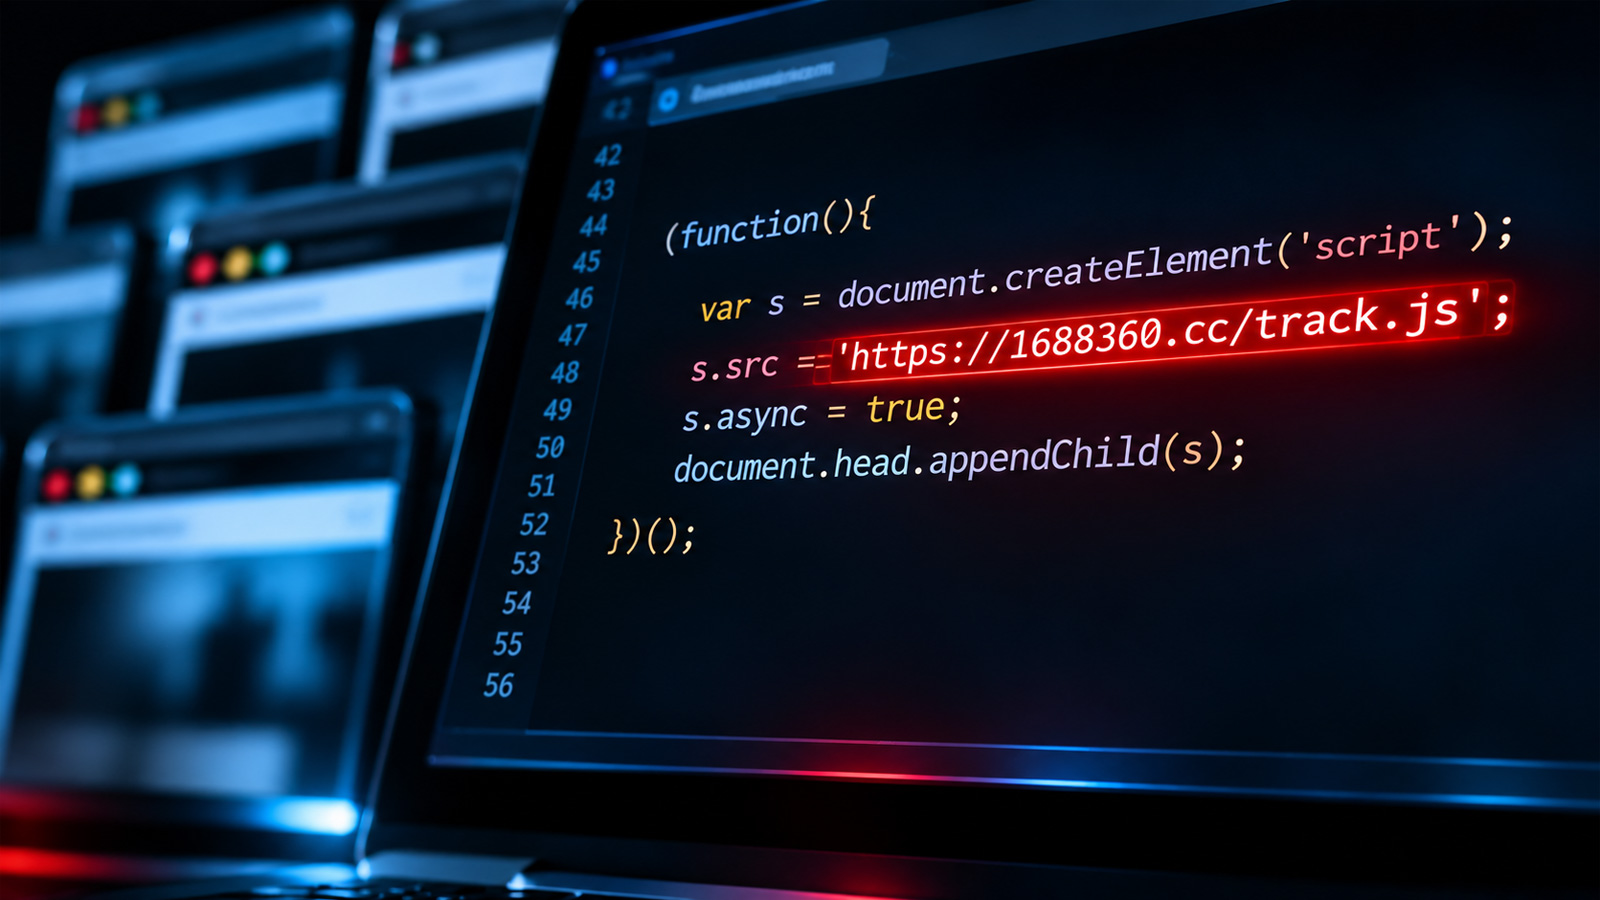
Analysis of the modified Optimizely files showed that attackers injected code that attempted to load an additional JavaScript payload from:
1688360[.]cc/track.js
Different versions of the malicious loader used several techniques, including:
- Direct references to the remote payload.
- Base64-encoded URLs decoded with JavaScript
atob(). - Embedded fallback copies of malicious code if remote loading was blocked.
This redundancy increased the likelihood that the payload would execute even when one delivery method failed.
Malware Targeted Cryptocurrency Transactions
One of the primary capabilities of the injected JavaScript was cryptocurrency address replacement.
The malware monitored webpages for wallet addresses and attempted to replace legitimate addresses with attacker-controlled ones.
This technique can silently redirect cryptocurrency transfers because users often copy and paste long wallet addresses without manually verifying every character.
Wallets embedded in the malicious script had received approximately $7,000 in cryptocurrency transactions by November 16, although not all activity could be definitively attributed to this campaign.
Payment Card Skimming Added Financial Theft Risk
The malicious JavaScript also included web-skimming functionality designed to identify and capture:
- Payment card numbers.
- Expiration dates.
- Security codes.
Captured payment information could then be transmitted to attacker-controlled infrastructure.
This type of browser-side attack is especially dangerous because it occurs directly inside a trusted website, potentially bypassing user expectations and traditional perimeter defenses.
iOS Exploit Kits Delivered to Visitors
The campaign also attempted to deliver additional exploit code to Apple devices.
Researchers identified payloads associated with the Coruna and DarkSword exploit frameworks, which target different iOS versions.
This means the operation went beyond financial theft and attempted to exploit vulnerabilities on iPhones and iPads visiting affected websites.
Users running outdated versions of iOS or iPadOS were therefore potentially exposed to significantly higher risk.
Additional Data Collection Capabilities
The malicious track.js payload also contained functionality capable of collecting:
- Browser cookies.
- Visited webpage URLs.
- Screenshots.
Depending on the victim’s active sessions and browser state, this information could potentially expose authenticated sessions, sensitive page content, or other account-related data.
Optimizely Cleanup Reduced Exposure
The earliest observed malicious Optimizely injection appeared during the morning of November 16.
By later that day, remediation had removed nearly all known infected scripts, with only one of the previously identified compromised files still containing malicious code at the time of follow-up analysis.
However, the exact duration of the vulnerability and the total number of affected website visitors remain unclear.
What Users and Organizations Should Check
Users who visited affected websites during the incident window should review any cryptocurrency transfers to confirm that destination wallet addresses were not modified.
Anyone who entered payment-card details should monitor transactions and contact their card issuer if suspicious activity appears.
iPhone and iPad users should ensure that iOS and iPadOS are fully updated, particularly because the campaign attempted to deliver exploit frameworks targeting older software versions.
Organizations using third-party JavaScript platforms should also strengthen software supply-chain security by implementing strict Content Security Policy rules, Subresource Integrity where applicable, script monitoring, third-party dependency inventories, and rapid alerting for unexpected changes to externally hosted JavaScript.
Leave a Reply